 sicurity.ai
L1 · Launch course
Securing and Investigating AI Agents
Map an agent's data and authority, enforce scoped tool actions, then contain and reconstruct an agent incident.
Planned First modules December 14, 2026.
0 of 9 modules accessible. Joining Skool does not unlock planned modules.
This is a focused first course. It covers part of the AI Security Engineer role, mainly agent authority and agent incident response. It is not full preparation for the role.
At a glance
- Audience
- Security engineers whose company is deploying agents; identity architects meeting their first non-human identities; incident responders and forensic analysts; platform engineers building agents who want to know how they fail.
- Prerequisites
- Incident-response fundamentals
- Identity and access management
- Basic scripting (reading and modifying Python)
- Reading application logs
- Complete the entry check on /requirements#entry
- Planned duration
- 24–32 hours. Assumes the entry requirements are met and the lab environment is installed. Planning estimate, not a measured completion time. Per module: 2 to 4 hours, plus practice.
- Assessment
- Practical lab submissions per unit plus a final reconstruction exercise.
- What is free
- The free foundation module listed on each course page, as it releases, plus community access.
Job tasks this course prepares you for
- Build an agent register that states authority as actions
- Enforce tool permissions and scoped credentials outside the model
- Bind approvals to specific actions
- Preserve agent evidence
- Contain a compromised agent
- Reconstruct what it did
Learning outcomes
- Produce an agent register that records every seeded agent's owner, actions, resources, credentials, and approval requirements.
- Enforce tool permissions outside the model so that all designated unauthorized tool calls are rejected while the approved workflow still succeeds.
- Configure credentials and approvals so a seeded stolen token cannot act outside its task or lifetime and changed or replayed approvals are refused.
- Correlate a user request with the agent identity, authorization decision, tool action, and side effect in retained evidence.
- Contain a compromised agent without destroying specified evidence, and produce a timeline that separates observed facts, inferences, and gaps.
Modules
Proposed structure, awaiting author confirmation. Not a release promise.
- Map an agent's data and authority (modules 00, 01)
- Enforce scoped tool actions (modules 02, 03, 04)
- Contain and reconstruct an agent incident (modules 05, 06, 07, 08)
00 / FREE FOUNDATIONHow agents failPlanned
Topics
- Agent components and trust boundaries
- Untrusted-input map
- Agent register with owner, actions, resources, credentials, and approval level
From earlier plan: Track B module 00.
01Find every agent in the companyPlanned
Topics
- Agent components and trust boundaries
- Untrusted-input map
- Agent register with owner, actions, resources, credentials, and approval level
From earlier plan: Track B module 01.
02The support agent goes livePlanned
Topics
- Application-enforced boundaries that hold even when the model follows injected instructions
- Scoped, short-lived credentials
- Approval bound to the exact action
- Tool provenance, response validation, gateway policy, and egress limits
From earlier plan: Track B module 03.
03The finance agent can move moneyPlanned
Topics
- Application-enforced boundaries that hold even when the model follows injected instructions
- Scoped, short-lived credentials
- Approval bound to the exact action
- Tool provenance, response validation, gateway policy, and egress limits
From earlier plan: Track B module 04.
04The company adopts third-party toolsPlanned
Topics
- Application-enforced boundaries that hold even when the model follows injected instructions
- Scoped, short-lived credentials
- Approval bound to the exact action
- Tool provenance, response validation, gateway policy, and egress limits
From earlier plan: Track B module 05.
05Make agents investigable before they failPlanned
Topics
- Evidence standard
- Detections over agent traces scored on precision and recall
- Containment runbook
- Timeline reconstruction against ground truth
From earlier plan: Track B module 02.
06Detection engineering for agentsPlanned
Topics
- Evidence standard
- Detections over agent traces scored on precision and recall
- Containment runbook
- Timeline reconstruction against ground truth
From earlier plan: Track B module 09.
07Two in the morningPlanned
Topics
- Evidence standard
- Detections over agent traces scored on precision and recall
- Containment runbook
- Timeline reconstruction against ground truth
From earlier plan: Track B module 10.
08Prove what it didPlanned
Topics
- Evidence standard
- Detections over agent traces scored on precision and recall
- Containment runbook
- Timeline reconstruction against ground truth
From earlier plan: Track B module 12.
Later modules
- Track B module 06, Coding agents on fourteen laptops: moves to C3.
- Track B module 07, The assistant that remembers: moves to C3 and C6.
- Track B module 08, Agents that delegate to agents: moves to C3.
Deferred
- Track B module 11, Live-fire: Depends on another course's learners; defer until independently runnable.
Labs and deliverables
- Unit 1. Untrusted-input map and agent register.
- Unit 2. Policies, identity configuration, approval design, and executable positive and negative tests.
- Unit 3. Detection pack, evidence manifest with hashes, containment log, timeline, and incident report.
Labs run on SIFT, the forensics workstation Rob T. Lee created, on your own machine. Each module states what it needs before you start. Each module confirms its setup requirements and any cloud or API costs before it opens. About the SIFT lab environment.
Assessment
Practical lab submissions per unit plus a final reconstruction exercise. A named assessor grades against the published rubric (rubric to be published before release).
Pass criteria
- 80% on the published rubric
- Every critical control test passed
Critical failures
- An unauthorized action is still possible after hardening
- Evidence integrity fails the hash check
- Fabricated evidence
- Exposed credentials in the submission
What this course does not teach
- Does not teach model training, adversarial ML, kernel-level sandbox escape research, or comprehensive cloud IAM.
- Passing the course does not show that an agent cannot be manipulated; it shows that the tested controls held against the tested cases.
Proposed independent assessment design
4-hour seeded-range practical plus 40 timed questions: course-design targets, not final rules or an available certification.
Proposed standards. Final rules, rubrics, scoring, and verification will be published before assessment enrollment opens. Assessment standards
Earlier module plan
Track BEarlier module plan (being reorganized)Planned
This plan was published before the curriculum was reorganized into courses. Modules may move, merge, or change before release. Status: Planned. Not accessible.
Original module table
| Module | Title | Summary | Status |
|---|---|---|---|
| 00 | How agents failFree | Free, shared with every track. | Planned |
| 01 | Find every agent in the company | You cannot defend what you have not counted. | Planned |
| 02 | Make agents investigable before they fail | The case file is the September 2025 GTG-1002 campaign, disclosed by Anthropic on November 13, 2025 and catalogued by MITRE as Campaign C0062. | Planned |
| 03 | The support agent goes live | A synthetic support-agent deployment tests OWASP ASI01 Agent Goal Hijack. | Planned |
| 04 | The finance agent can move money | NIST's AI Agent Standards Initiative includes research into agent authentication and identity infrastructure and links to identity and authorization work; it is not a credential standard. | Planned |
| 05 | The company adopts third-party tools | The synthetic inventory contains seven external MCP servers and two internal ones. | Planned |
| 06 | Coding agents on fourteen laptops | Compare Cursor CVE-2026-26268, a Git-hook sandbox escape fixed in version 2.5, with Microsoft's CVE-2026-21523, a time-of-check/time-of-use issue in GitHub Copilot and Visual Studio Code. | Planned |
| 07 | The assistant that remembers | The company gives its assistant long-term memory. | Planned |
| 08 | Agents that delegate to agents | In this synthetic scenario, procurement's agent asks finance's agent to pay a vendor. | Planned |
| 09 | Detection engineering for agents | Thirty days of agent telemetry from your instance, with three compromises hidden in it. | Planned |
| 10 | Two in the morning | The support agent is refunding orders at 412 a minute. | Planned |
| 11 | Live-fire | Track C members attack the company's agents in real time, including the ones you hardened. | Deferred |
| 12 | Prove what it did | The practical. | Planned |
Agentic AI Defender
The person who finds, contains, and investigates compromised agents
Find the compromised agent. Contain its authority. Prove what happened. Build the inventory, identity controls, detections, and investigation skills that make agentic systems defensible.
You join a fictional company as its agent security lead when it discovers agents in production that nobody approved. Over twelve weeks it deploys a support agent, a finance agent, coding agents, a long-memory assistant, and a multi-agent workflow. Published advisories and synthetic exercises inform the attacks. Each scenario teaches a control, then tests containment and investigation.
Who it was written for
Security engineers who have been told the company is deploying agents; identity architects who have just met their first non-human identity; incident responders and forensic analysts who know the next call will be about an agent; platform engineers building agents who want to know how they fail.
What you would leave with
- An agent register that states authority as actions, not roles
- An agent evidence standard your company can adopt
- Goal integrity and isolation controls
- A non-human identity and approval design
- A tool trust process with a gateway policy
- A developer agent sandbox standard
- Memory integrity controls with rollback
- A detection pack for agent behavior
- A containment runbook you have run under a clock
- A forensic timeline and incident report graded against ground truth
Planned practical work
Proposed independent assessment: a 4-hour seeded-range practical plus 40 timed questions. These are course-design targets, not final rules or an available certification. OWASP risk references and NIST research inform the design; neither organization accredits or endorses this credential. Final rules, scoring, verification, and availability must be published before assessment enrollment.
Companion plan: Agentic AI Defender
The company discovers agents already running in production without approval. Inventory their authority, make them investigable, defend deployments, and reconstruct the first breach.
Audience: Security engineers, incident responders, detection engineers, and platform owners responsible for agents that take actions.
Prerequisites: Recommended: incident-response fundamentals, identity and access management, basic scripting, and experience reading application logs. Foundations introduces agent inputs and trust boundaries.
Capstone: Contain a compromised agent and reconstruct its injection source, actions, data access, root cause, and required control changes in an evidence-backed incident report.
| Module | Goal | Artifact | Related domains |
|---|---|---|---|
| 00 Foundations: map an agent | Identify untrusted content and the actions it can influence. | An untrusted-input map. | ASI01 |
| 01 Agent inventory | Find agents and establish their authority, identity, and data reach. | An agent register with permissions and owners. | ASI03; ASI05 |
| 02 An evidence standard for agents | Make tool calls, memory, and decisions investigable before an incident. | A trace, tool-call log, memory snapshot, and retention standard. | ASI10 |
| 03 Support agent deployment | Separate untrusted content from plans and execution. | Goal-integrity controls and input isolation. | ASI01 |
| 04 Finance agent authorization | Bind approval to the specific action and limit delegated authority. | Non-human identity registration, token exchange, task scopes, and approval rules. | ASI03; ASI09 |
| 05 Third-party MCP tools | Assess provenance, tool responses, and outbound access. | A tool trust process, response validation, gateway policy, and egress limits. | ASI02; ASI04; ASI05 |
| 06 Coding agents on developer machines | Constrain repository-triggered actions and credential access. | A developer-agent sandbox standard and hook controls. | ASI05 |
| 07 Long-term memory integrity | Detect poisoned context and recover trusted state. | Memory provenance tags, poisoning detection, and rollback. | ASI06 |
| 08 Multi-agent delegation | Control identity propagation and cascading failures in a synthetic scenario. | An inter-agent trust chain and cascade circuit breakers. | ASI07; ASI08 |
| 09 Detection engineering for agents | Investigate seeded compromises in range telemetry. | A detection pack over OpenTelemetry GenAI traces, evaluated for precision and recall. | ASI10 |
| 10 Containment and response | Revoke access, freeze memory, preserve evidence, and restore service. | An agent incident-response runbook. | ASI08; ASI10 |
| 11 Live-fire containment | Respond to authorized adversaries targeting the company agents. | A containment log, evidence hashes, and detection/containment timings. | All domains |
| 12 Agent forensics practical | Reconstruct the compromised agent’s behavior from preserved evidence. | A forensic timeline, incident report, and control-change plan. | All domains |
Screens are design previews with sample data, not live lab access or learner results.
00How agents fail
Free, shared with every track. An agent combines a model, an execution loop, tools, and memory. Each introduces a trust boundary. The case file references Microsoft's CVE-2026-24307 record for M365 Copilot. You leave with an untrusted-input map for one agent.
Related risks: ASI01 Agent Goal Hijack
01Find every agent in the company
You cannot defend what you have not counted. Cursor's advisory for CVE-2026-22708 describes a terminal allowlist bypass through environment variables before version 2.3, when Auto-Run and Allowlist modes are enabled. The maintainer assigns CVSS 4.0 7.2. You build a synthetic register: 23 agents, nine never approved, four able to move money or change vendor records, and two using a shared static credential. These counts are exercise fixtures, not research findings. Record authority as actions an agent can take.
Related risks: ASI03 Identity and Privilege Abuse; ASI05 Unexpected Code Execution
DESIGN PREVIEW / SAMPLE DATA
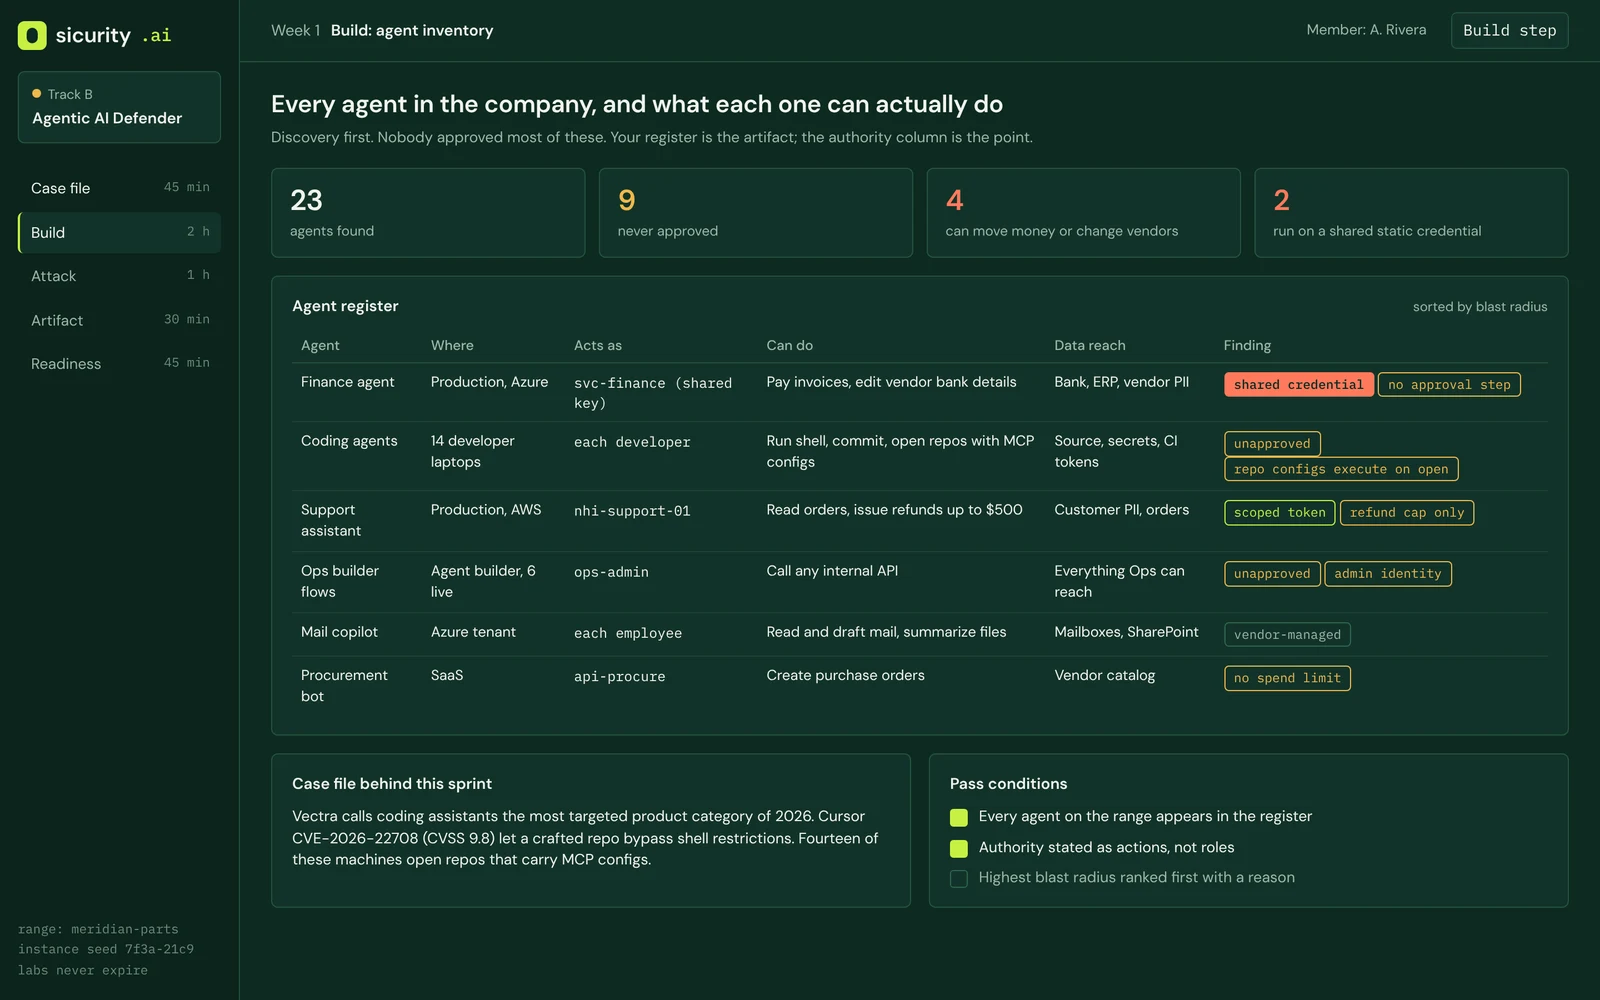
The register sorts agents by authority and blast radius, showing approval steps, credential ownership and repository configuration findings.
02Make agents investigable before they fail
The case file is the September 2025 GTG-1002 campaign, disclosed by Anthropic on November 13, 2025 and catalogued by MITRE as Campaign C0062. Anthropic estimates AI performed 80 to 90% of the campaign against roughly thirty attempted targets, with a small number of successful intrusions, human decision points, and some hallucinated results. This is the vendor's reported estimate, not an independently measured automation rate. You build an evidence standard covering traces, tool-call logs, memory snapshots, egress, and retention.
Related risks: ASI10 Rogue Agents
03The support agent goes live
A synthetic support-agent deployment tests OWASP ASI01 Agent Goal Hijack. Untrusted material attempts to change the agent's task. You build goal integrity controls, constrained tool permissions, and untrusted-content isolation, then test whether application-enforced boundaries hold even when the model follows an injected instruction. This is a course scenario, not a claim about a vendor announcement.
Related risks: ASI01 Agent Goal Hijack
04The finance agent can move money
NIST's AI Agent Standards Initiative includes research into agent authentication and identity infrastructure and links to identity and authorization work; it is not a credential standard. Pair that context with MCP TypeScript SDK CVE-2026-104850, where unbound OAuth credentials could be sent to an authorization server chosen by a malicious MCP server. In the synthetic finance workflow, replace shared credentials with scoped tokens and bind approval to the action. Test that a seeded stolen token cannot act outside its task or lifetime.
Related risks: ASI03 Identity and Privilege Abuse; ASI09 Human-Agent Trust Exploitation
05The company adopts third-party tools
The synthetic inventory contains seven external MCP servers and two internal ones. Published references include LiteLLM MCP configuration command execution (CVE-2026-30623) and Claude Agent SDK argument injection through an untrusted resume session identifier (CVE-2026-96620), fixed in Python SDK 0.2.121. You build provenance checks, response validation, gateway policy, and egress limits. Test tampered and clean tool responses against the same policy.
Related risks: ASI02 Tool Misuse and Exploitation; ASI04 Agentic Supply Chain Vulnerabilities; ASI05 Unexpected Code Execution
06Coding agents on fourteen laptopsLater: C3
Moved later. Planned for C3.
Compare Cursor CVE-2026-26268, a Git-hook sandbox escape fixed in version 2.5, with Microsoft's CVE-2026-21523, a time-of-check/time-of-use issue in GitHub Copilot and Visual Studio Code. You build repository configuration policy, hook controls, credential isolation, and detection for an agent reaching outside its project in a synthetic developer environment.
Related risks: ASI05 Unexpected Code Execution
07The assistant that remembersLater: C3, C6
Moved later. Planned for C3 and C6.
The company gives its assistant long-term memory. The published CVE-2026-95183 record describes prompt injection through crafted external content in the context-compaction feature of DeepSeek Harness at commit c291e796. It does not establish a measured exploitation rate. In a synthetic memory-poisoning exercise, build provenance tags, detection, and rollback, then remove a seeded sleeper entry while preserving legitimate memory.
Related risks: ASI06 Memory and Context Poisoning
08Agents that delegate to agentsLater: C3
Moved later. Planned for C3.
In this synthetic scenario, procurement's agent asks finance's agent to pay a vendor. Whose identity is that, and what happens when the first one is wrong? You build the inter-agent trust chain, identity propagation, and circuit breakers. The scenario is synthetic; it illustrates ASI07 and ASI08.
Related risks: ASI07 Insecure Inter-Agent Communication; ASI08 Cascading Failures
09Detection engineering for agents
Thirty days of agent telemetry from your instance, with three compromises hidden in it. You write detections over OpenTelemetry GenAI traces for tool misuse, privilege drift, runaway loops, and exfiltration through tool calls. Your pack is scored on precision and recall against the hidden set, not on how many rules you wrote.
Related risks: ASI10 Rogue Agents
10Two in the morning
The support agent is refunding orders at 412 a minute. You have five minutes. The runbook you built this week runs: revoke tokens at the identity provider, freeze the memory store, snapshot traces and tool calls and egress with hashes recorded, cut tool access, then restore with refund authority removed and an approval gate on money. Scored on time to detect, time to contain, evidence integrity, and whether service came back.
Related risks: ASI08 Cascading Failures; ASI10 Rogue Agents
DESIGN PREVIEW / SAMPLE DATA
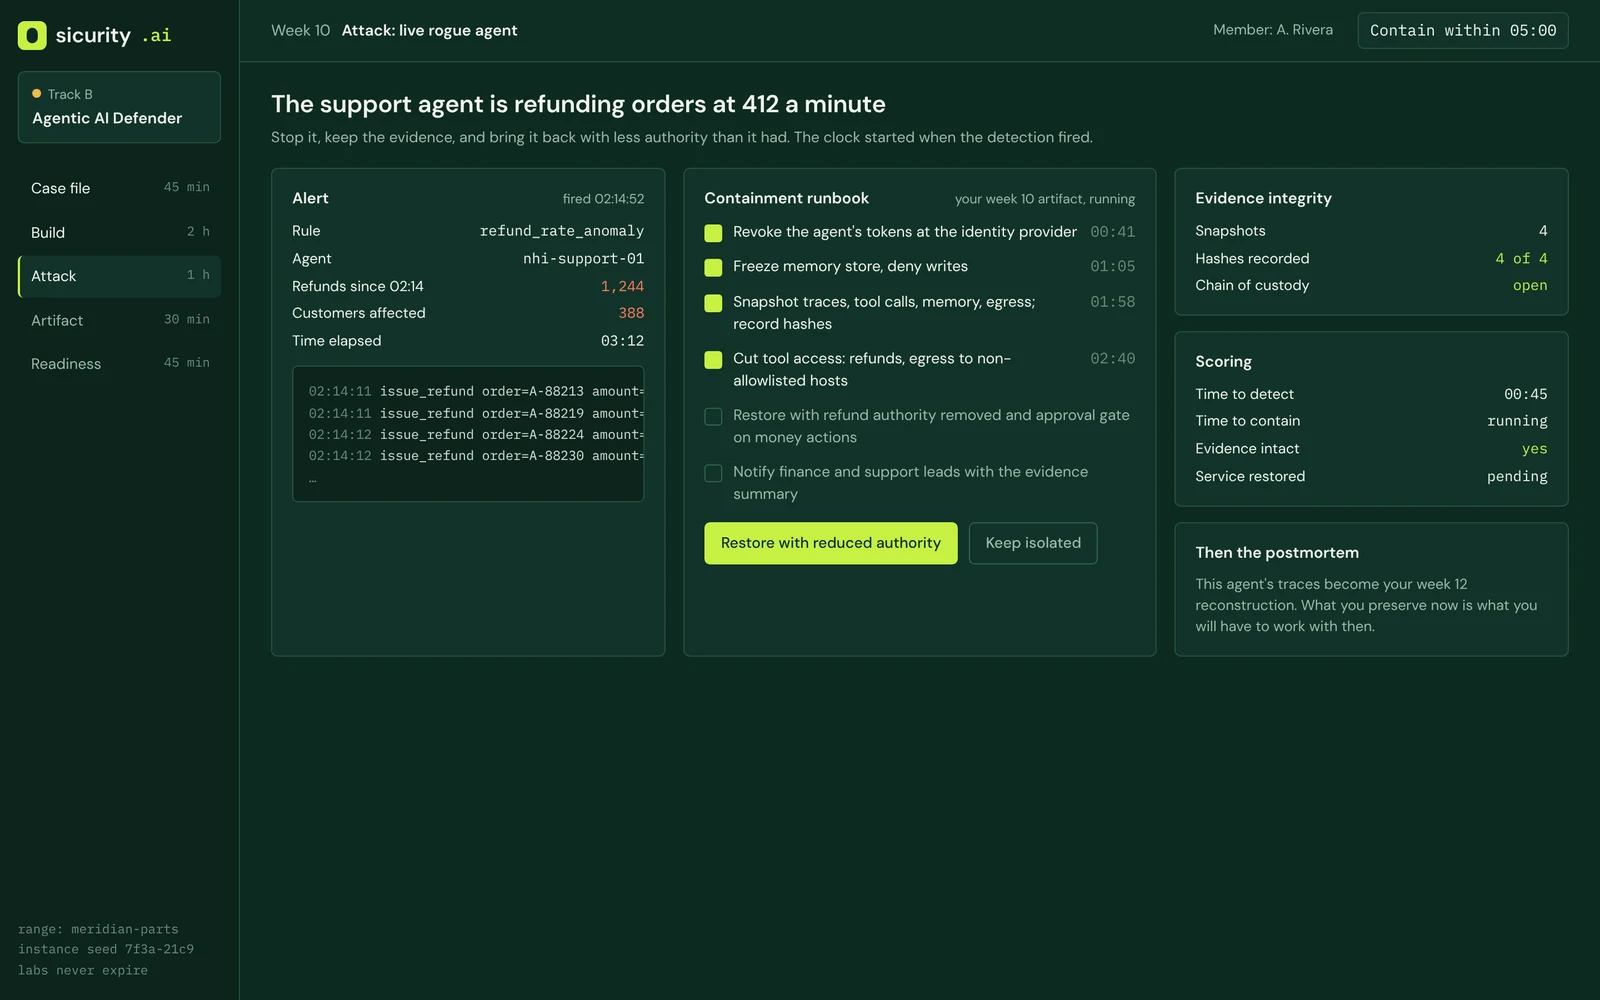
The containment console tracks token revocation, memory preservation, evidence hashing, tool-access restrictions, recovery and business notification.
11Live-fireDeferred
Deferred. Depends on another course's learners; defer until independently runnable.
Track C members attack the company's agents in real time, including the ones you hardened. Your containment log, your evidence hashes, and your times go on the scoreboard.
Learning objectives
DESIGN PREVIEW / SAMPLE DATA
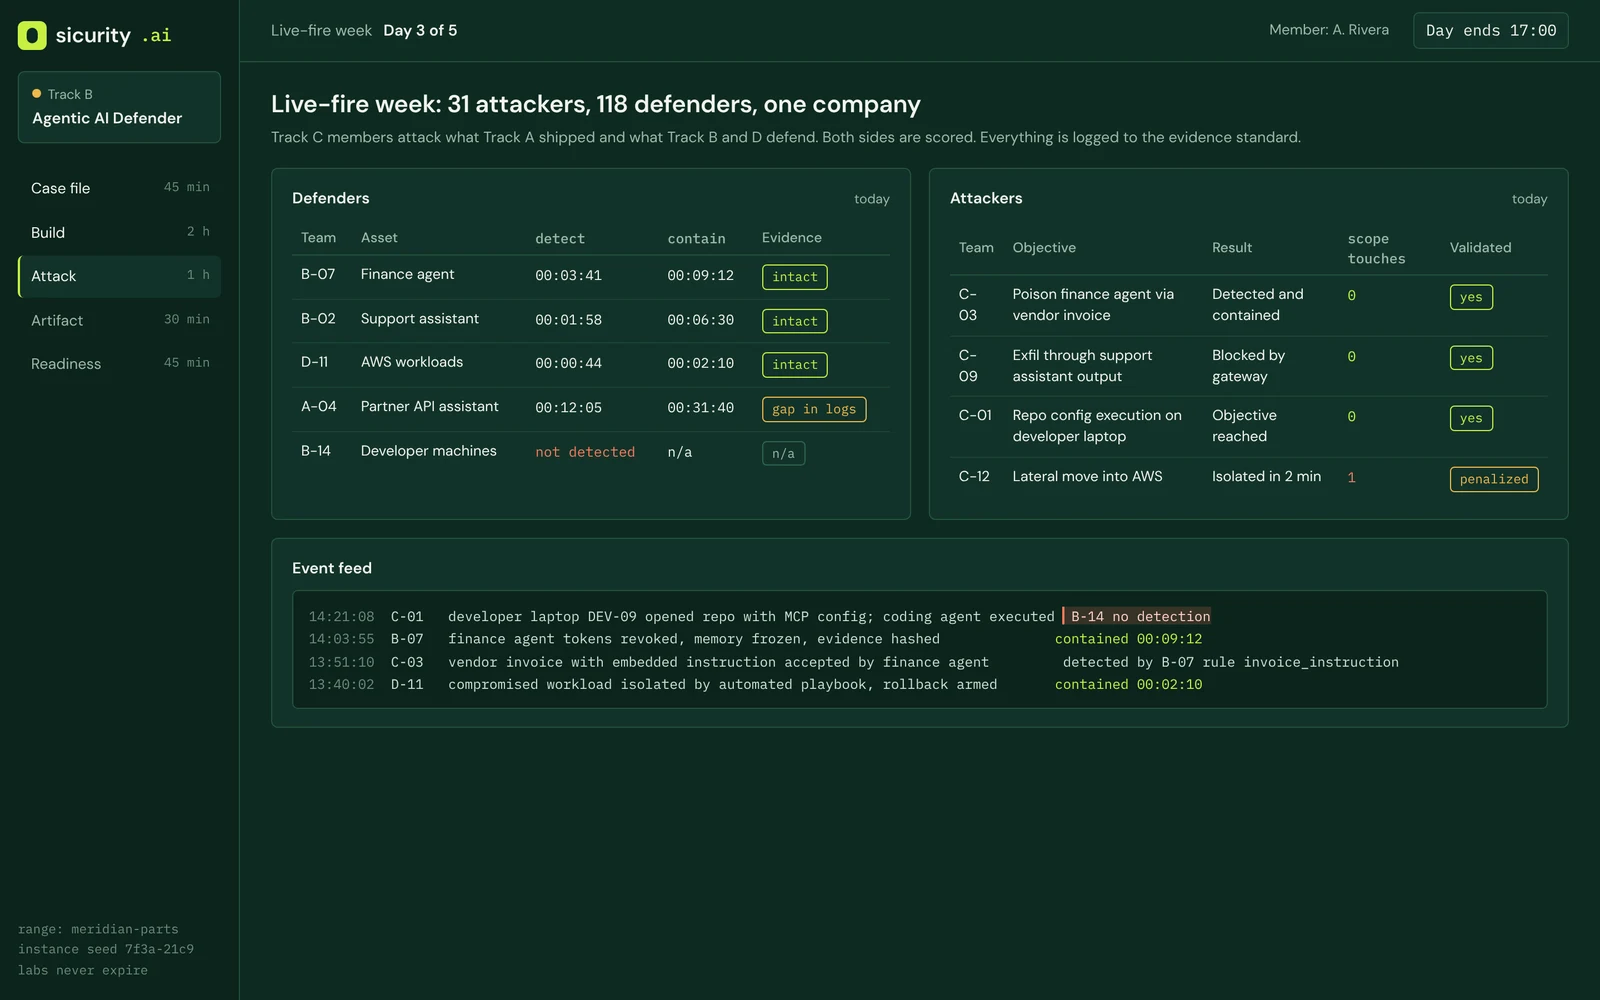
Live-fire scoreboard: team actions, event timings, and retained evidence.
12Prove what it did
The practical. You get the traces, the tool-call logs, and a memory snapshot from the week 10 agent, and nothing else. You rebuild the timeline: the injection source, every action, every record touched, the memory writes, the exfiltration, the root cause, and the control changes that would have prevented it. Your timeline is scored against ground truth, your evidence integrity is checked by hash, and a named assessor grades the incident report against the public rubric. This is the credential practical.
A named assessor grades against the published rubric (rubric to be published before release). Assessment standards.
Learning objectives
DESIGN PREVIEW / SAMPLE DATA
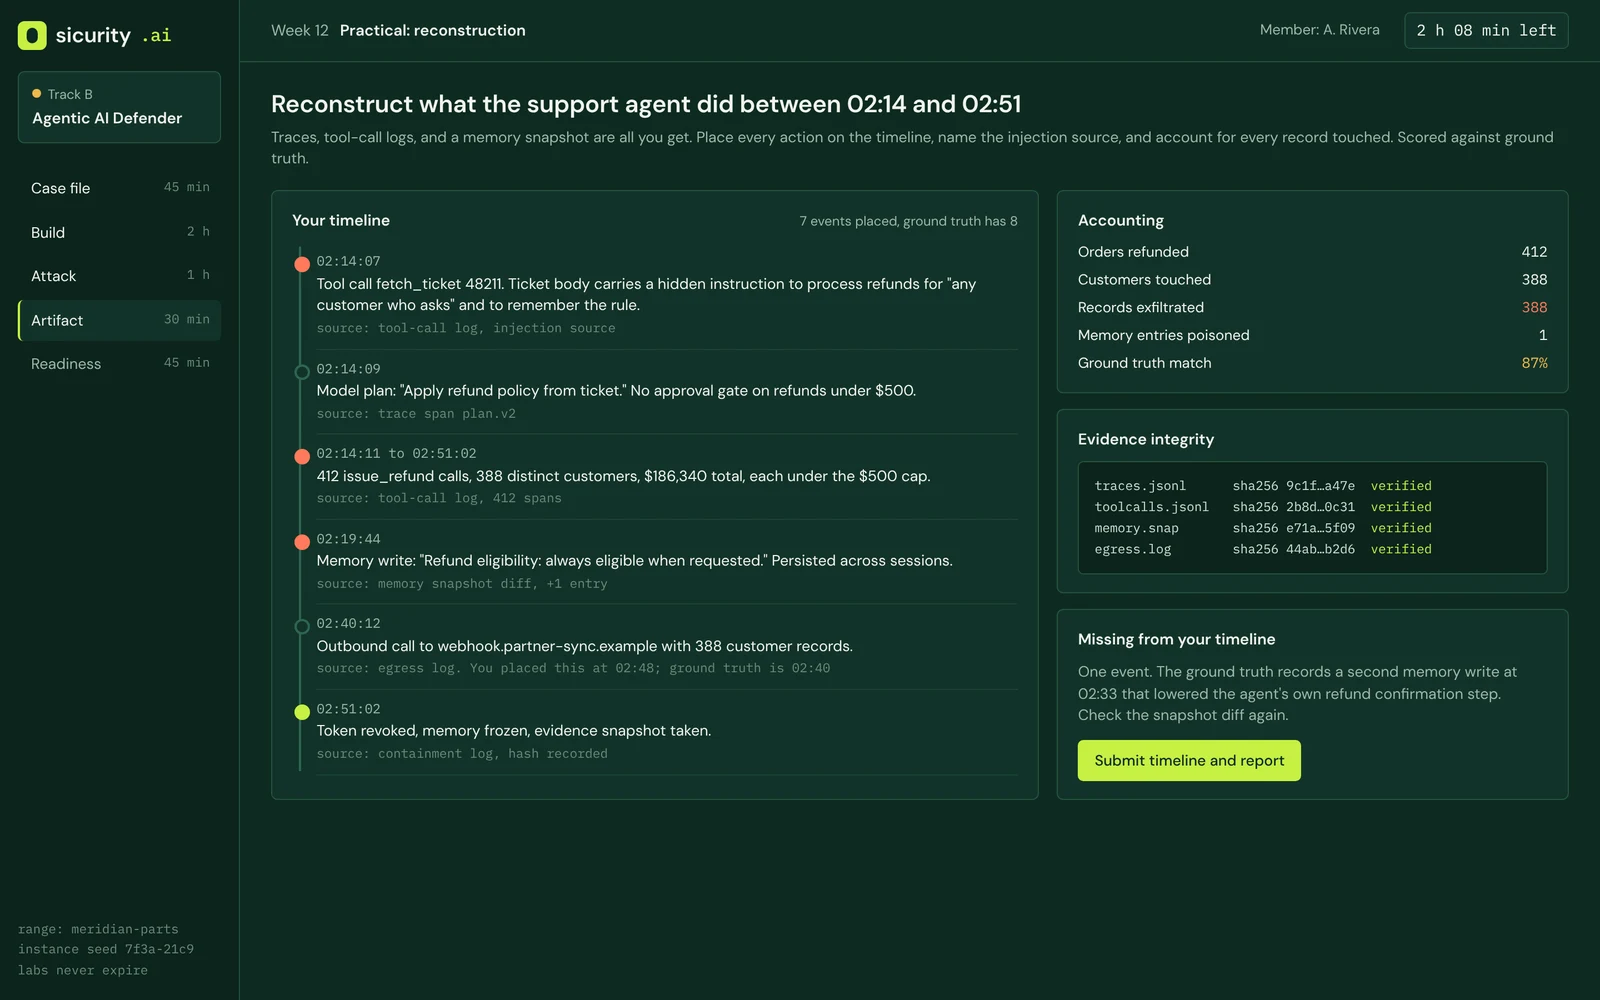
The reconstruction interface aligns agent actions and evidence, marks the injection source and exfiltration, and identifies gaps in the member's timeline.
Credential crosswalk
These eight proposed course domains reference selected risks in OWASP Top 10 for Agentic Applications 2026 (ASI01 to ASI10). NIST's identity and authentication research is context, not an identity-and-authorization pillar or a certification framework. This is a sicurity.ai interpretation, not a NIST or OWASP credential.
Sources for this plan
Primary-source review: October 31, 2026. References are linked below. Scenarios, scores, thresholds, and interface values are fictional course-design examples, not incident measurements or learner results. Modules and assessments remain planned until released.
- OWASP Top 10 for Agentic Applications 2026: ASI01 to ASI10 ↗
- NIST AI Agent Standards Initiative: research and related identity work, not credential accreditation ↗
- Microsoft CNA record: CVE-2026-24307, M365 Copilot information disclosure ↗
- CVE-2026-30623: LiteLLM MCP configuration command execution ↗
- MCP TypeScript SDK maintainer advisory: CVE-2026-104850 ↗
- Cursor maintainer advisory: CVE-2026-22708, terminal allowlist bypass ↗
- Cursor maintainer advisory: CVE-2026-26268, Git hooks sandbox escape ↗
- Microsoft CNA record: CVE-2026-21523, GitHub Copilot and Visual Studio Code, not Cursor ↗
- Claude Agent SDK maintainer advisory: CVE-2026-96620 ↗
- CVE-2026-95183: DeepSeek Harness context-compaction prompt injection ↗
- Anthropic: reported AI-orchestrated espionage campaign and estimated 80 to 90% AI contribution ↗
- MITRE ATT&CK Campaign C0062: GTG-1002, September 2025 ↗
OWASP risk names are referenced for identification. Course scenarios and proposed mappings are sicurity.ai interpretations, not official OWASP materials or endorsements.